In the AI Training Skool AI Governance Pay Index, 65 named US employers cited ISO/IEC 42001 in 71 of 179 AI governance job postings (40%), collected from Indeed in early October 2026. Technology and software companies posted the most of these roles (26), followed by financial services (13) and professional services firms (13). Most were manager or analyst roles in GRC, risk and engineering teams.
| ISO/IEC 42001 in US job postings | Value |
| Postings that name ISO/IEC 42001 | 71 of 179 (40%) |
| Named employers behind those postings | 65 (one posting gave no employer name) |
| Largest sector (our classification) | Technology, software and AI: 26 postings |
| Largest role family | GRC, compliance and AI governance: 21 postings |
| Most common level | Manager, lead, principal or staff: 28 postings |
| Remote roles | 14 of 71 (20%), against 16% of all 179 postings |
| States with at least one posting | 21 states plus the District of Columbia |
| Postings that ask for an ISO/IEC 42001 credential by name | 3 |
| Median advertised pay midpoint, 43 postings with pay | $168,000 |
Source: AI Training Skool AI Governance Pay Index, US Indeed postings.
Which US Employers Name ISO/IEC 42001 in Job Postings?
ISO/IEC 42001 appears in postings from household names such as Bank of America, Cisco, Salesforce, Verizon and Palo Alto Networks, and from many smaller firms. The table lists 59 of the 65 named employers with the role each one posted and the month it was posted.
We left out six: three employers that sell compliance or risk software and three staffing agencies hiring for an unnamed client. The table also skips the posting with no employer name and a job board’s repost of the Verizon role already in the list. Postings close and change, so treat each row as a lead to check, not an open vacancy.
| Employer | Role title in the posting | Location | Posted | Sector (our classification) |
| Adobe | Sr Technology Compliance Product Owner | San Jose, CA | September | Technology, software and AI |
| Aegis AI | GRC Engineer | Not stated | October | Technology, software and AI |
| Blue Yonder | Staff Security Analyst II (GRC) | Dallas, TX | August | Technology, software and AI |
| ButterflyMX | GRC Engineer | Remote | August | Technology, software and AI |
| Cisco | Strategy and Planning Manager, Enterprise AI Programs and Governance | Research Triangle Park, NC | October | Technology, software and AI |
| Cvent | Senior Analyst, Security Risk and Compliance (AI Risk Governance) | Tysons Corner, VA | September | Technology, software and AI |
| Deepgram | Compliance and Documentation Lead | Remote | October | Technology, software and AI |
| Doppel | Director, Governance, Risk and Compliance | Not stated | September | Technology, software and AI |
| GitLab | Senior Security Risk Engineer; Staff Security Governance Engineer, Policies and Standards | Remote | September and October | Technology, software and AI |
| Granicus | GRC Automation Engineer | Remote | August | Technology, software and AI |
| Klaviyo | Lead Security Compliance Engineer | Boston, MA | September | Technology, software and AI |
| Medidata Solutions | Privacy and RAI Engineer | New York, NY | September | Technology, software and AI |
| Mercor | Security GRC Lead | San Francisco, CA | September | Technology, software and AI |
| Palo Alto Networks | Principal GRC Business Engineer | Santa Clara, CA | August | Technology, software and AI |
| Parloa | Senior IS&T Governance Partner | New York, NY | August | Technology, software and AI |
| Salesforce | Technology Auditor, Internal Audit | Dallas, TX | October | Technology, software and AI |
| ServiceNow (Moveworks) | Staff Security Engineer (Compliance) | Mountain View, CA | August | Technology, software and AI |
| Sysdig | Trust and Assurance Lead | Remote | September | Technology, software and AI |
| Tricentis | Director, Security Governance, Risk and Compliance | Austin, TX | September | Technology, software and AI |
| Vasion | Privacy and AI Governance Analyst | Lehi, UT | August | Technology, software and AI |
| Wrapbook | GRC Principal, Data Privacy and Security | Remote | September | Technology, software and AI |
| Bank of America | Sr Data Architect, AI Controls, Governance and Capabilities | Charlotte, NC | September | Financial services and insurance |
| BankUnited | Technology Risk, Cyber Governance and Third-Party Risk Manager | Miami Lakes, FL | September | Financial services and insurance |
| DAI Companies | Sr Manager, Governance, Risk, Compliance and Privacy | Plano, TX | August | Financial services and insurance |
| dv01 | Data Governance Lead | New York, NY | September | Financial services and insurance |
| Envestnet | Lead Security Governance Partner, Assurance | Berwyn, PA | September | Financial services and insurance |
| Kapitus | Principal Data and AI Governance Architect | Arlington, VA | September | Financial services and insurance |
| Mizuho | AI Risk and Governance Lead | New York, NY | September | Financial services and insurance |
| Moody’s | VP, AI Risk Management | New York, NY | September | Financial services and insurance |
| Navy Federal Credit Union | Senior Quantitative Risk Analyst (Internal Audit, Model and AI Governance) | Pensacola, FL | October | Financial services and insurance |
| Rockefeller Capital Management | AI Engineer, Controls and Capability Enablement | Hamilton Township, NJ | September | Financial services and insurance |
| T. Rowe Price | Senior Manager, Technology and Cyber Risk Management | Owings Mills, MD | September | Financial services and insurance |
| WesBanco Bank | SVP and Director of IT Governance, Cyber Security | Wheeling, WV | September | Financial services and insurance |
| Arnall Golden Gregory | Information Governance Specialist | Atlanta, GA | September | Professional services |
| Crowe | Financial Services AI Governance Consulting Manager | Denver, CO | September | Professional services |
| Cyber Advisors | AI and Data Governance Engineer | Maple Grove, MN | September | Professional services |
| Cyclotron | Sr. AI Governance Architect; AI and Data Governance Engineer | Remote | October | Professional services |
| Dentsu | AI Governance Analyst; AI Governance Engineer; AI Governance Concierge Service Lead | New York, NY | September | Professional services |
| Kroll | Manager, AI Assurance and Governance, Cyber Advisory | Not stated | August | Professional services |
| Mayer Brown | Manager, AI Security and Risk | Chicago, IL | September | Professional services |
| OneMagnify | Senior Lead, AI Governance | Remote | September | Professional services |
| Aya Healthcare | Sr. GRC Analyst | San Diego, CA | September | Healthcare and life sciences |
| Baylor Genetics | Sr Mgr Third Party Risk | Not stated | September | Healthcare and life sciences |
| Detego Health | Internal Enterprise Controls and Technology Assurance Auditor | Not stated | September | Healthcare and life sciences |
| Intuitive | IT Sr Director, Compliance and Risk Governance | Sunnyvale, CA | August | Healthcare and life sciences |
| LabConnect | Head of IT Governance, Risk, and Compliance (GRC) | Johnson City, TN | September | Healthcare and life sciences |
| MiniMed | Senior Principal Information Security Governance, Risk and Compliance Analyst | Northridge, CA | September | Healthcare and life sciences |
| Hitachi High-Tech America | AI Data and Security Governance Engineer | Hillsboro, OR | September | Industrial, energy, telecom and infrastructure |
| Johnson Controls | Associate Director, Data Governance Enablement | Milwaukee, WI | September | Industrial, energy, telecom and infrastructure |
| Oceaneering | AI Governance Intern | Houston, TX | September | Industrial, energy, telecom and infrastructure |
| Vantage | Cybersecurity AI Risk and Governance Director, Global | Sterling, VA | September | Industrial, energy, telecom and infrastructure |
| Verizon | Principal, Cybersecurity Audit, Risk and Governance Architect, AI and Emerging Tech | Ashburn, VA | September | Industrial, energy, telecom and infrastructure |
| Victaulic | Senior AI Risk Analyst | Pennsylvania | October | Industrial, energy, telecom and infrastructure |
| Carter’s | Governance, Risk and Compliance Manager (IT) | Atlanta, GA | September | Consumer, retail, media and real estate |
| Lennar | Director, Assistant General Counsel, Privacy | Miami, FL | August | Consumer, retail, media and real estate |
| Sony Interactive Entertainment | Responsible AI and Governance Technical Specialist | San Mateo, CA | September | Consumer, retail, media and real estate |
| General Dynamics Mission Systems | Senior AI Governance and Risk Specialist | Chantilly, VA | September | Government, defense, education and international |
| Nova Southeastern University | Security Governance, Risk, and Compliance Manager (hybrid, Florida) | Florida | September | Government, defense, education and international |
| World Bank Group | Senior Digital Specialist, Trustworthy AI (with Cybersecurity) | Washington, DC | October | Government, defense, education and international |
Source: AI Training Skool AI Governance Pay Index, 71 US Indeed postings that name ISO/IEC 42001. All posting months are in 2026. “Remote” follows the index rule: the posting’s location is Remote, or no city is given and the text says remote.
Only three employers posted more than one such role: Dentsu (three), and GitLab and Cyclotron (two each). Demand is spread thin across many employers, so a list of companies to watch beats waiting for one big hirer.
Of the Big Four accounting firms, only Deloitte appears in our sample, and neither of its two postings named ISO/IEC 42001. No posting in the 179 was for a chief AI officer.
ISO 42001 Hiring by Sector and Employer Type
Technology, software and AI companies posted 37% of the ISO/IEC 42001-naming roles in our data. Financial services and professional services followed with 18% each.
| Sector (our classification) | Postings | Share of 71 | Employers | Examples |
| Technology, software and AI | 26 | 37% | 24 | Adobe, Cisco, GitLab, Palo Alto Networks, Salesforce |
| Financial services and insurance | 13 | 18% | 13 | Bank of America, Mizuho, Moody’s, T. Rowe Price |
| Professional services (consulting, audit, law, agencies, staffing) | 13 | 18% | 10 | Crowe, Kroll, Dentsu, Mayer Brown |
| Industrial, energy, telecom and infrastructure | 7 | 10% | 6 | Verizon, Johnson Controls, Vantage, Victaulic |
| Healthcare and life sciences | 6 | 8% | 6 | Intuitive, MiniMed, Baylor Genetics |
| Consumer, retail, media and real estate | 3 | 4% | 3 | Carter’s, Lennar, Sony Interactive Entertainment |
| Government, defense, education and international | 3 | 4% | 3 | General Dynamics Mission Systems, World Bank Group |
Source: AI Training Skool classification of the 71 postings. Method: one sector per employer, by main business as stated in the posting’s company description. Software sold to a regulated industry (for example, clinical trial software) counts as technology. Staffing firms count as professional services unless the posting names the client’s industry. Verizon’s role appears twice in the data (once reposted by a job board), so the industrial row has seven postings and six employers. The technology row has 26 postings from 24 named employers, because GitLab posted two roles and one posting did not name its employer. Employer counts add to 65.
Technology companies lead because many sell AI features to enterprise buyers, and their postings tie the role to the company’s own certification or audit program. GitLab’s Senior Security Risk Engineer posting asks the hire to own AI impact assessments, AI risk assessments and risk treatment “to support ISO 42001 certification”. Cvent’s posting asks for support of “the ISO 42001 audit process end-to-end”.
Financial firms name the standard next to other frameworks: 12 of their 13 postings also named a NIST framework, and three cited the SR 11-7 model risk guidance. Consultancies name it because they assess client readiness. Kroll’s posting lists assessing clients “against frameworks such as NIST AI RMF, EU AI Act, ISO 42001”.
Which Roles and Levels Ask for ISO/IEC 42001?
GRC, risk and engineering roles carry most ISO/IEC 42001 demand. Engineering roles are the most likely to name it: of 18 engineering and architecture postings in the index, 13 (72%) named the standard, against 1 of 20 counsel roles.
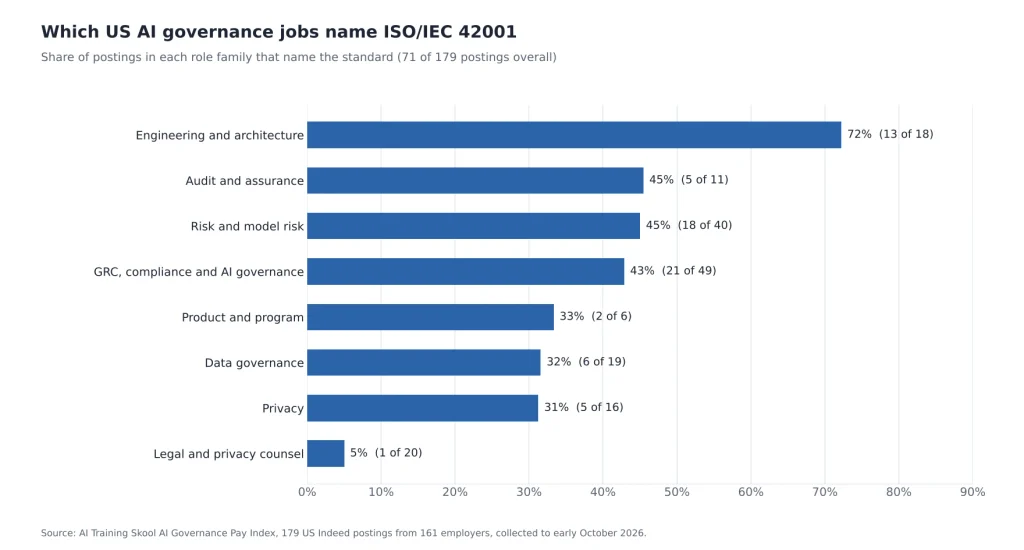
Share of US AI governance postings naming ISO/IEC 42001 by role family: engineering and architecture 72% (13 of 18), audit and assurance 45% (5 of 11), risk and model risk 45% (18 of 40), GRC, compliance and AI governance 43% (21 of 49), product and program 33% (2 of 6), data governance 32% (6 of 19), privacy 31% (5 of 16), legal and privacy counsel 5% (1 of 20)
| Role family | All postings | Name ISO/IEC 42001 | Share of the family |
| GRC, compliance and AI governance | 49 | 21 | 43% |
| Risk and model risk | 40 | 18 | 45% |
| Engineering and architecture | 18 | 13 | 72% |
| Data governance | 19 | 6 | 32% |
| Audit and assurance | 11 | 5 | 45% |
| Privacy | 16 | 5 | 31% |
| Product and program | 6 | 2 | 33% |
| Legal and privacy counsel | 20 | 1 | 5% |
| Level | All postings | Name ISO/IEC 42001 | Share of the level |
| Analyst, specialist, engineer or associate | 50 | 21 | 42% |
| Senior individual contributor | 23 | 13 | 57% |
| Manager, lead, principal or staff | 63 | 28 | 44% |
| Director and associate director | 22 | 5 | 23% |
| VP, head, chief or executive director | 21 | 4 | 19% |
Source: AI Training Skool AI Governance Pay Index, 179 US postings. Level and role family come from the job title.
Titles hide most of this demand. Only 31 of the 71 postings (44%) put “AI” or “RAI” in the job title; the rest read as GRC engineer, security risk engineer, technology auditor or compliance manager. The duties these roles share are decoded in AI governance officer duties in real US postings.
Postings that named the standard had a $168,000 median advertised midpoint, against $169,000 for those that did not. The standard defines the work, not the pay. Pay by level, role family and state is set out in what AI governance roles pay in the US.
What Employers Want You to Do With ISO/IEC 42001
In 29 of the 71 postings, ISO/IEC 42001 is part of the work itself: running the employer’s own certification, advising clients, or aligning controls to the standard. In the other 42 it is knowledge the employer requires or would like.
| How the posting uses ISO/IEC 42001 | Postings | Example from a posting |
| Run or support the employer’s own ISO/IEC 42001 certification, audit or compliance program | 11 | GitLab, Cvent, Doppel, Baylor Genetics, Vasion |
| Advise clients on ISO/IEC 42001 readiness | 4 | Crowe, Kroll, Cyclotron, World Bank Group |
| Align controls, map frameworks or track the standard as a named duty | 14 | Verizon, Moody’s, WesBanco Bank, Victaulic |
| Required knowledge or experience in the qualifications | 19 | Blue Yonder, Mizuho, Salesforce, Hitachi High-Tech America |
| Preferred, “a plus” or “nice to have” | 22 | Cisco, Dentsu, Palo Alto Networks, Bank of America |
| Something an intern will learn | 1 | Oceaneering |
Source: AI Training Skool reading of the 71 postings. Each posting is counted once, under its strongest use of the standard.
Lead Implementer and Lead Auditor Wording in US Postings
Only 3 of the 71 postings named an ISO/IEC 42001 Lead Implementer or Lead Auditor certification, all as preferred: Nova Southeastern University, Kroll and one compliance-software vendor. Six named an ISO/IEC 27001 Lead Implementer or Lead Auditor credential instead, a sign that many of these teams grew out of information security programs.
If you are weighing a credential, read what a Lead Implementer certificate covers under ISO/IEC 42001. The AIGP, CISSP and CRISC appear more often in these ads, and AI governance certifications compared sets them side by side.
Do ISO 42001 Certified Companies Hire for It?
Some do. Three of the companies on our list of US organizations reporting ISO/IEC 42001 certification posted ISO 42001-naming roles in this window: Salesforce, ServiceNow (for its Moveworks unit) and Doppel. The others in the 40-company list are in a sourced list of ISO 42001 certified companies.
Other postings show employers working toward a certificate or keeping one. Vasion’s mentions “ISO 42001 certification maintenance”, and Cvent’s asks for AI management system artifacts “required for ISO 42001 certification and ongoing surveillance audits”. ButterflyMX’s asks the hire to scope “a readiness path for ISO 42001”.
Before you name a company’s certificate in an interview, check it. The ISO Help Centre notes that ISO itself does not perform certification and points to IAF CertSearch, a database of accredited certificates. IAF itself was succeeded by Global Accreditation Cooperation on 1 January 2026, and the database still carries the IAF name.
Where the ISO 42001 Jobs Are: States and Remote Share
California and New York had the most ISO/IEC 42001-naming postings (eight each), followed by Virginia (six) and Texas (five). One in five of these roles (14 of 71) was remote, a higher share than the 16% across all AI governance postings in the index.
| State | Postings naming ISO/IEC 42001 | All AI governance postings in the index | Share naming the standard |
| California | 8 | 20 | 40% |
| New York | 8 | 19 | 42% |
| Virginia | 6 | 12 | 50% |
| Texas | 5 | 13 | 38% |
| Florida | 4 | 6 | 67% |
| North Carolina, Pennsylvania, Georgia, Illinois | 2 each | 7, 4, 4, 3 | Mixed |
| District of Columbia | 1 | 9 | 11% |
| 12 other states | 1 each | Not shown | Not shown |
| Remote | 14 | 28 | 50% |
| Location not stated | 5 | Not shown | Not shown |
Source: AI Training Skool AI Governance Pay Index, US Indeed postings. Virginia’s six include the Verizon role counted twice.
Washington, DC is the outlier: nine AI governance postings, but only one named ISO/IEC 42001. If you live outside the large hubs, the remote row matters most, because half of the remote AI governance roles in our data named the standard.
What Else ISO 42001 Postings Ask For
ISO/IEC 42001 rarely travels alone in a posting. Nearly three in four of these postings (73%) also named the NIST AI Risk Management Framework, and more than half named ISO/IEC 27001.
| Also named in the posting | Share of the 71 ISO/IEC 42001 postings | Share of the 108 other postings |
| NIST AI Risk Management Framework | 73% (52) | 18% (19) |
| ISO/IEC 27001 | 54% (38) | 9% (10) |
| SOC 2 | 45% (32) | 7% (8) |
| CISSP | 45% (32) | 15% (16) |
| GDPR | 44% (31) | 21% (23) |
| EU AI Act | 42% (30) | 9% (10) |
| CRISC | 35% (25) | 10% (11) |
| CISM | 34% (24) | 10% (11) |
| HIPAA | 30% (21) | 10% (11) |
| NIST Cybersecurity Framework | 28% (20) | 6% (6) |
| CIPP (any) | 27% (19) | 15% (16) |
| PCI DSS | 23% (16) | 2% (2) |
| AIGP | 20% (14) | 9% (10) |
| ISO/IEC 27701 | 14% (10) | 1% (1) |
| OWASP AI security guidance (mostly the Top 10 for LLM Applications) | 14% (10) | 0% |
Source: AI Training Skool AI Governance Pay Index. We did not count CISA, because the same letters name the US Cybersecurity and Infrastructure Security Agency and our check found the agency in at least two postings.
In practice, an ISO/IEC 42001 posting is usually a security GRC posting with AI added. The NIST AI Risk Management Framework, released on 26 January 2023 for voluntary use, is the most common companion, so learn to map between the two.
If ISO/IEC 42001 is the line you cannot yet show on your resume, our ISO/IEC 42001 Lead Implementer training for people applying to these roles costs US$795, awards 32 CPD hours and includes two exam attempts.
State AI laws barely show up. No posting in the 179 named Texas’s Responsible Artificial Intelligence Governance Act, which took effect on 1 January 2026, and only one named Colorado’s AI law. For background, see the overview of regulation of artificial intelligence in the United States.
How to Search Job Boards for ISO 42001 Roles Yourself
Search the number, not the title. In our data, 47 of the 71 postings wrote “ISO 42001” and 24 wrote “ISO/IEC 42001”, some inside lists such as “ISO 27001/27017/27018/42001”. A search for “42001” alone catches all of them. Queries that worked on the employment websites we used:
- “42001” on its own, set to the US or to remote, sorted by date.
- “42001” plus a family word: “42001 GRC”, “42001 risk”, “42001 audit” or “42001 privacy”. This finds the 40 of 71 roles without “AI” in the title.
- “AI management system”, which appeared, spelled out or as the acronym AIMS, in 7 of the 71 postings and in none of the others.
- Company career pages: check the employers in the table above and the certified companies every few weeks.
Set alerts on queries 1 and 2. If you do not yet have the experience these ads ask for, start with getting into AI governance without direct experience.
Is Demand for ISO 42001 Skills Growing?
One snapshot cannot show a trend. It does show breadth: 65 named employers across seven sectors and 21 states plus DC asked for the standard in about two months of postings. Government projections for the feeder jobs point up. The BLS Occupational Outlook Handbook projects employment of information security analysts to grow 21% from 2025 to 2035, with a $129,180 median in May 2025. Many security GRC teams hire from that occupation.
The routes into these roles, by background, are mapped in AI governance careers for US professionals.
Frequently Asked Questions
Which Companies Hire for ISO 42001 Skills in the US?
In our October 2026 Pay Index, 65 named US employers listed ISO/IEC 42001 in AI governance job postings. They include Bank of America, Cisco, Salesforce, Verizon, Palo Alto Networks, Moody’s, Mizuho, Kroll and Crowe. Technology companies posted 26 of the 71 roles, financial services 13 and professional services 13.
What Jobs Ask for ISO/IEC 42001?
GRC, risk and security engineering roles ask for ISO/IEC 42001 most. In our data, 21 of the 71 postings naming it were GRC and compliance roles, 18 were risk roles and 13 were engineering and architecture roles. Typical titles were GRC Engineer, AI Risk and Governance Lead, Technology Auditor and Senior Security Risk Engineer.
Do Employers Require an ISO 42001 Lead Implementer Certification?
Rarely. Only 3 of 71 US postings naming ISO/IEC 42001 asked for an ISO/IEC 42001 Lead Implementer or Lead Auditor credential, and all three listed it as preferred. Employers screen for the skill: 29 postings put the standard in the duties, and 19 listed knowledge of it as a requirement.
Are ISO 42001 Jobs Remote?
Some are. In our data, 14 of the 71 US postings naming ISO/IEC 42001 (20%) were remote, compared with 16% of all 179 AI governance postings in the index. Remote employers included GitLab, Sysdig, Deepgram and Granicus. Half of all remote AI governance postings named the standard.
Which Industries Need ISO 42001 Skills?
Technology and software companies posted 37% of the ISO/IEC 42001-naming roles in our data. Financial services and professional services each posted 18%. Healthcare, industrial, consumer and public-sector employers made up the rest.